RASP analysis: Android and iOS internals
Reversing runtime protections on both platforms, identifying what they detect and miss, and building and improving detections.
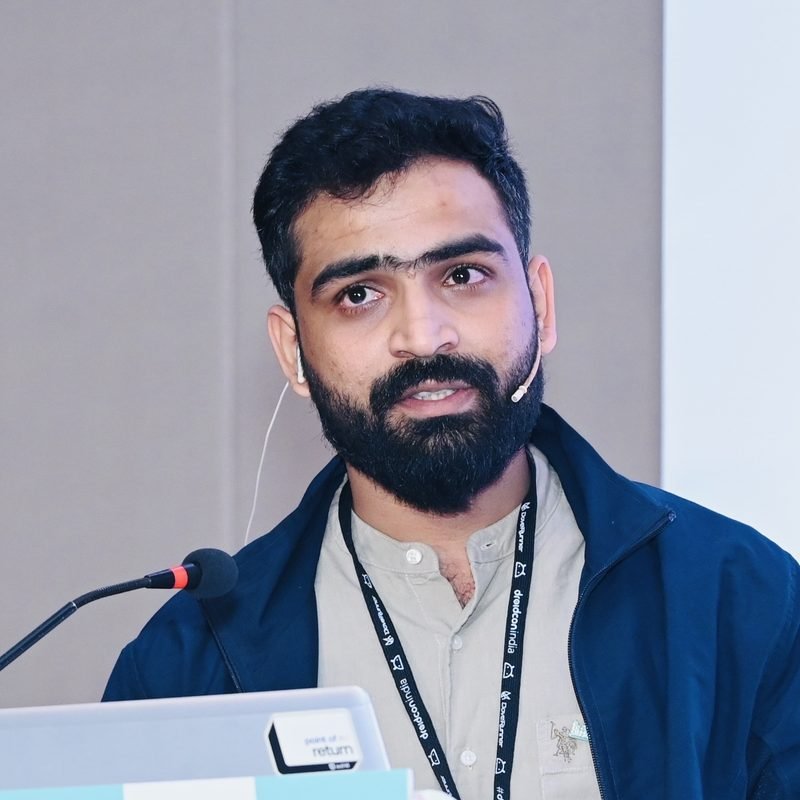
Principal Security Architect · Doverunner
8+ years in application security. Today I work across product and internal security, specializing in mobile RASP, OS internals and content security. I break things to find what's exposed, then build the detections and controls that fix it.
Interactive: query this portfolio like an API.
Host: sidharth.sec
Accept: application/json
User-Agent: recruiter/1.0
or Ctrl+Enter
{
  "name": "Sidharth B Nair",
  "role": "Principal Security Architect",
  "company": "Doverunner Inc",
  "location": "Kochi, Kerala, India",
  "years": "8+",
  "focus": ["product security", "internal security", "RASP detections", "multi-DRM content security"]
}
01 Summary
I'm a Principal Security Architect at Doverunner, working across product and internal security. On the product side I analyze RASP and build detections for it, alongside multi-DRM content security. Internally the scope runs from vulnerability management and incident response to identity and access, monitoring, cloud security, compliance, third-party risk and DLP. I joined in 2023 as a Senior Threat Analyst and moved into this role in June 2026.
Before Doverunner I led internal pentesting and third-party risk at Nykaa, and spent over four years doing application security consulting at SISA for clients across industries, most of them in banking and financial services. Across all of it the aim is the same: find what breaks early, and build the controls that keep it fixed.
I've spoken at droidcon India 2025 on secure mobile apps and at ISACA Silicon Valley on Log4Shell exploitation and mitigation, and I've done bug bounty research since 2016.
Pentesting and VAPT, SAST/DAST and source code review across web and thick-client applications.
API pentesting and review as part of web and mobile assessments for clients across industries, with a focus on banking and financial services.
RASP analysis and detection building on Android and iOS, grounded in platform internals and reverse engineering.
Multi-DRM content security at Doverunner, including VAPT and vulnerability research on multi-DRM integrated platforms.
Threat modeling and architecture reviews early in design, secure SDLC integration, SAST/DAST testing frameworks, CI/CD security checks, and security training for development teams.
Vulnerability management, incident response, identity and access, security monitoring, cloud and infrastructure security, DLP, awareness programs reporting to executive leadership, and remediation across teams.
Security policy, compliance and audits including PCI-DSS, third-party and vendor risk assessments, and security architecture reviews.
Bug bounty since 2016, vulnerability research, and talks at droidcon India and ISACA Silicon Valley.
02 Experience
03 Talks & research
Reversing runtime protections on both platforms, identifying what they detect and miss, and building and improving detections.
Conference talk on building secure mobile apps, delivered at droidcon India 2025.
Webinar on the Apache Log4j vulnerability (CVE-2021-44228, CVSS 10.0): live exploitation, impact and mitigation.
Company-wide presentation at SISA on the Apache Log4j vulnerability and what it means for an organization.
Responsible disclosures through HackerOne, with acknowledgments from Fitbit and AlienVault Security.
VAPT on multi-DRM integrated platforms. Recurring issues: unbound tokens and replayable requests, client-trusted device and DRM tier, missing entitlement checks, unvalidated signed URLs, and exposed keys on software-only clients.
04 Toolkit
05 Contact
Open to senior application and product security roles. Based in Kochi, Kerala, India.
Phone: available on request by email